Almost 9 in 10 firms exposed to cyber risks remain vulnerable for six months or longer
Published:
Read Time: 3 mins
Some of the world’s largest firms are leaving critical security weaknesses unaddressed for months, despite fixes being available, according to a new study from cyber risk analytics provider KYND.
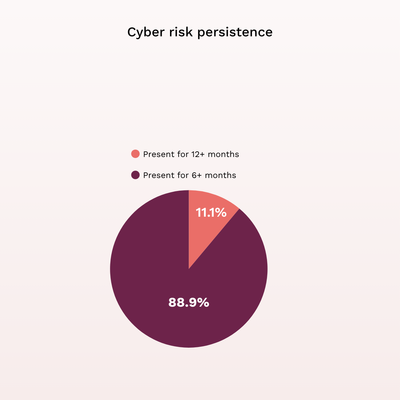
The analysis of more than 2,000 organisations — including companies from the FTSE 350 and the S&P 500 — found that 11 per cent were exposed to actively exploited vulnerabilities. Of those, almost nine in ten (88 per cent) remained exposed for six months or longer. Actively exploited cyber risks are security vulnerabilities or weaknesses that attackers are currently taking advantage of in real-world attacks.
KYND’s cyber analysts discovered risks affecting a wide range of critical infrastructure and enterprise software, with exposure spanning from web applications and popular platforms such as Oracle, WordPress and Apache to the networking hardware and secure communication protocols that businesses rely on daily. These findings underscore widespread delays in essential maintenance and an ongoing gap between detecting and fixing vulnerabilities.
According to Andy Thomas, KYND’s CEO and Founder, leaving cyber risks unaddressed can have serious consequences beyond IT security – as insurers look to refine their pricing and risk assessment models, remediation speed and patch management practices are becoming key indicators of an organisation’s overall cyber resilience.
He said: “A company’s approach to patching tells you a lot about its approach to risk.
“As demand for cyber coverage continues to grow, cyber insurers are increasingly recognising that it’s not just the number of vulnerabilities that matters, but how quickly critical vulnerabilities are addressed. When exposure lasts for months, it’s rarely a one-off — it’s a behavioural signal that an organisation struggles with remediation in general.
“Across a portfolio, the same slow-to-fix firms remain persistently vulnerable, exposures stack up over time, and the insurer’s true risk can look very different from a point-in-time snapshot.”
KYND's analysis focused on vulnerabilities known to be actively exploited in the wild. By leaving these highest-tier risks open for months, organisations are potentially inviting significant breaches rather than managing minor nuisances.
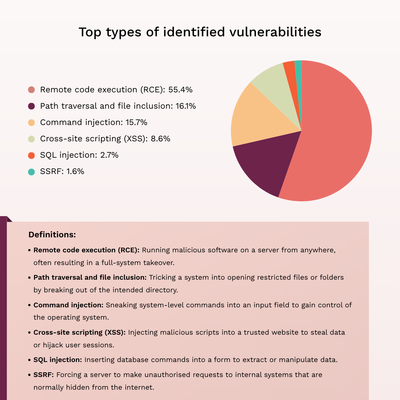
The most prevalent class of vulnerability identified was remote code execution (RCE), which accounted for 31 per cent of the top vulnerability types analysed. This flaw enables attackers to run malicious commands on a target system without physical access or valid credentials.
The scale of this risk has been underscored by recent events. In October 2025, a critical flaw in Microsoft Windows Server Update Services (CVE-2025-59287) was exploited, enabling attackers to gain full control of unpatched servers.
Thomas added: “The Microsoft Windows server incident prompted emergency updates from Microsoft and urgent advisories from CISA, highlighting how quickly threat actors can move when known weaknesses remain unaddressed.
“Such vulnerabilities can be exploited to steal data, deploy malware, or disrupt operations — turning preventable flaws into serious business risks.”
For more information, please visit: www.kynd.io
Ends
Editors notes
KYND is a pioneering cyber risk management provider which supports businesses of all sizes and portfolios across the insurance and financial services industries worldwide. Headquartered in London, with offices in Portugal and the US, KYND transforms complex cyber risk data into clear, actionable insights, making it quicker and easier to assess, manage and mitigate risk with confidence.
Its innovative technology provides instant visibility into cyber risk exposure and offers continuous monitoring with advanced real-time threat alerts. KYND’s flexible, made-to-measure product suite delivers jargon-free insights with tools and bespoke advice to support businesses, insurance underwriters, brokers, advisors and investment managers.
Founded in 2018, KYND has been recognised in the InsurTech 100 list for four years running and scooped Cyber Product of the Year at the National Insurance Awards 2025.
For more information, please visit: https://www.kynd.io/
Follow KYND on LinkedIn: @KYNDCyber