Five ways businesses can prepare now for the Cyber Security and Resilience Bill
Published:
Read Time: 5 mins
Organisations are being urged to prepare now for tougher cyber security rules, as the Cyber Security and Resilience Bill enters its final stages in the House of Lords.
The proposed law is the biggest update to the UK's cyber security rules since the Network and Information Systems (NIS) Regulations came into force in 2018. Managed IT service providers and data centres will be regulated for the first time, and regulators will gain powers to designate critical suppliers. Organisations that experience a reportable cyber incident will need to send an initial report within 24 hours of becoming aware of it.
Enforcement is also getting tougher. Organisations that fail to meet their legal cyber security obligations could face fines of up to £17 million or 4% of their worldwide turnover, whichever is higher.
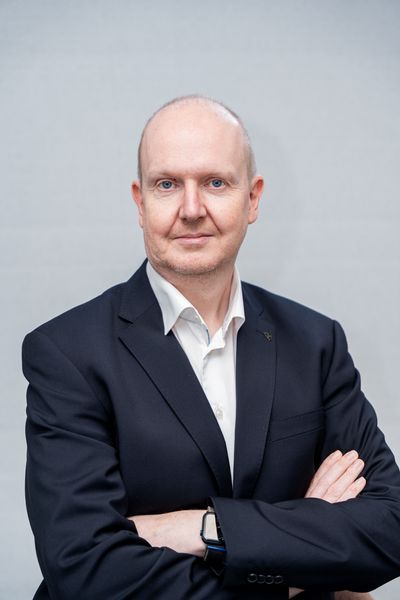
David Robinson, head of cyber security at Restore Information Management, warns that organisations that wait for the Bill to become law before reviewing their cyber security risk being caught unprepared. That includes smaller suppliers whose customers will be regulated under the new rules.
He said: “Cyber resilience cannot be achieved at the last minute. Fixing weak infrastructure, improving supplier oversight and building reliable recovery processes can take years. Any business that starts these processes when the Bill becomes law will already be behind – and could end up facing significant fines for that mistake.”
Here are five ways businesses can act now to prepare for the Cyber Security and Resilience Bill.
1. Check whether your organisation comes under the scope of the new regulations
It’s not enough to wait and see whether your organisation is covered once the regulations become law. Medium and large managed service providers will fall into scope automatically. The Bill will also give regulators, such as the Information Commissioner’s Office (ICO) and Ofcom, powers to designate suppliers as critical where their disruption could seriously affect essential or digital services. Designated suppliers then take on direct security and reporting duties, even if they are smaller businesses.
Businesses should identify who their likely regulator will be and which parts of their own operations will be covered.
Organisations outside the direct scope should not assume the changes are irrelevant to them either. If a business has customers that are regulated under the new law, those customers may introduce stricter security and reporting requirements throughout their supply chains.
David added: “If customers rely on your services to keep essential systems running, you need to prepare for greater scrutiny. Waiting for a regulator to inform you that you’re affected will leave too little time to address weaknesses.”
2. Conduct a gap analysis
Once a business has identified its obligations under the law, it needs to assess whether its existing arrangements for a cyber-attack or security breach will meet the new requirements. Areas to consider include data governance, risk management, how breaches are detected, access controls and recovery.
David said: “Organisations can compare their current operations against the proposed requirements, existing Network and Information Systems (NIS) obligations and the National Cyber Security Centre’s (NCSC) Cyber Assessment Framework to identify weak spots and the impact they will have on the business.”
Weaknesses that could interrupt critical services, or prevent an organisation from detecting, investigating and reporting an incident quickly, should take priority.
David added: “A gap analysis needs to lead to action. A list of weaknesses with no commitment won’t make an organisation more resilient – it’s crucial to establish whose responsibility it will be to correct areas of weakness and get things up to scratch.”
3. Prepare for 24-hour incident reporting
Under the Bill, an initial incident report will be due within 24 hours of an organisation becoming aware of an incident, with a fuller report within 72 hours. The definition of a reportable incident is also wider than before, covering incidents capable of having an adverse effect on services, not only those that already have.
Organisations that fail to meet their obligations under the Bill could face fines of up to £17 million or 4% of worldwide turnover, whichever is higher, for the most serious breaches, or up to £10 million or 2% of worldwide turnover for less serious ones.
Businesses need to establish a 24-hour on-call rota, or an equivalent system, along with clear escalation criteria and an agreed framework for deciding whether an incident needs to be reported. Contact details for regulators and the NCSC should be up to date and accessible during a breach.
4. Map out critical information and suppliers
While businesses will naturally focus on internal systems, it’s important they establish where critical information is stored externally, who can access it, how it moves between systems and how quickly it can be recovered after an incident.
David said: “Businesses need to identify where their dependencies on external suppliers are, so that in the event of a breach everyone is on the same page. An organisation may have its own strong internal response plan, but it could still fail in the event of a breach if a critical supplier takes too long to raise the alarm.”
Organisations need to set up clear pathways with suppliers for incident notification, investigation support and access to evidence. Otherwise, they will be left with little time to understand their exposure and meet their own reporting obligations.
5. Test plans under pressure
A written plan will not prove that an organisation can recover from a serious security breach. Businesses need to run realistic exercises involving data loss, disruption to physical infrastructure and ransomware to ensure they can withstand a breach.
Some exercises should take place at night and over the weekend, when fewer employees and suppliers are available, to simulate a live attack. Teams need to test whether they can contain the threat, still access critical information, report the incident to the correct parties and maintain essential services.
David added: “The middle of a cyber-attack is the worst possible time to discover that backups can’t be restored, an emergency contact is out of date, or nobody knows who the breach needs to be reported to. Plans need to be tested under pressure, not just approved.”
For more information, please visit: https://www.restore.co.uk/informationmanagement/
Ends
Editors notes
For more information, please contact:
Fran Herring, Rose Lock or Alex Hankinson
Midnight Communications
T: 01273 666 200
Notes to editors
About Restore Information Management
Restore Information Management is the largest UK-owned provider of information management services, specialising in secure physical document storage, digital transformation and data management.
Its solutions help organisations protect, transform and access their information seamlessly and efficiently. With a strong focus on innovation and customer-centric delivery, Restore Information Management enables businesses to streamline operations and remain competitive in a fast-moving digital landscape.
Restore Information Management is trusted by more than 6,000 clients across the UK, including more than 80% of NHS trusts. It is also a recognised leader in ESG, achieving a CDP ‘A rating’ in 2026, placing it in the top 4% of businesses in the UK for carbon reduction.