Cleafy identifies mobile malware before formal classification
Published:
Read Time: 2 mins
New Cleafy capability enables banks to identify and respond to emerging mobile malware before a formal signature exists. Already in production for more than a year, 99.9% of its early detections were subsequently confirmed as true positives.
MILAN, Italy – 14 September 2026 – Cleafy, the fraud prevention company, today announced a new capability that identifies malicious mobile activity in real-time, even before a formal signature is published. This enables banks and payment operators to act on emerging mobile threats during the critical period before traditional security systems know what they are looking for.
Already running in production at a major European bank for more than a year, 99.9% of Cleafy’s early detections have subsequently been confirmed as true positives, while 96% of threats later confirmed as malicious had already been identified by Cleafy.
The capability addresses a growing challenge for fraud teams. Generative AI enables criminal developers to produce new variants of banking malware in hours rather than weeks, each one starting without a signature or entry in any threat feed. Kaspersky recorded a 188% surge in NFC relay attacks on smartphones in the first four months of 2026 alone, driven by malware families including SuperCard X, PhantomCard and NGate.
Traditional malware defences rely on recognising known threats. New or modified malware must therefore be discovered, analysed and classified before those systems know what they are looking for – a process that can take hours or days. Fraud does not wait for classification.
When SuperCard X was first uncovered in April 2025, antivirus engines did not yet recognise it, but it was already relaying stolen card data in live fraud operations.
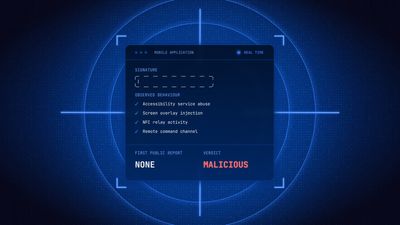
Cleafy has developed Mobile Malware Early Detection to identify applications consistent with mobile malware before a formal classification is available.
When suspicious behaviour is identified, fraud teams receive a real-time signal that can be used within their existing controls – for example, to trigger additional authentication, hold a transaction for further checks or place an account under closer monitoring.
Each detection is delivered with a human-readable explanation – including the suspected malware family, relevant permissions and the evidence behind the detection – so analysts see why something has been flagged, rather than receiving a score or verdict alone.
Carmine Giangregorio, co-founder and Product Manager at Cleafy, said:
“For thirty years the industry has asked: ‘What is this malware called?’ The more important question is: ‘What is happening on this device, and do we have enough evidence to act?’
“Until now, banks have had two imperfect options for handling unknown threats: wait for classification and risk fraud losses, or intervene early and risk unnecessary customer friction.
“Mobile Malware Early Detection gives banks the intelligence to make that decision sooner and with greater confidence – reducing fraud without unnecessarily adding friction to the customer experience.”
Mobile Malware Early Detection works with Cleafy Cloud customers’ existing rules, policies and integrations, allowing banks to incorporate the new intelligence into their existing fraud operations. A phased rollout to Cleafy Cloud customers will begin in September 2026.
For more information about Cleafy for fraud prevention, visit www.cleafy.com.
Ends
Editors notes
Cleafy is the fraud management platform for banks, trusted by over 183 financial institutions and protecting 250 million end users worldwide. Its modular architecture spans attack prediction, real-time detection and response, autonomous investigation, workforce protection, and global threat intelligence. Nyx is Cleafy's autonomous investigation and defence optimisation product. Founded in Milan, with offices in Rome and London.
For more information visit www.cleafy.com